


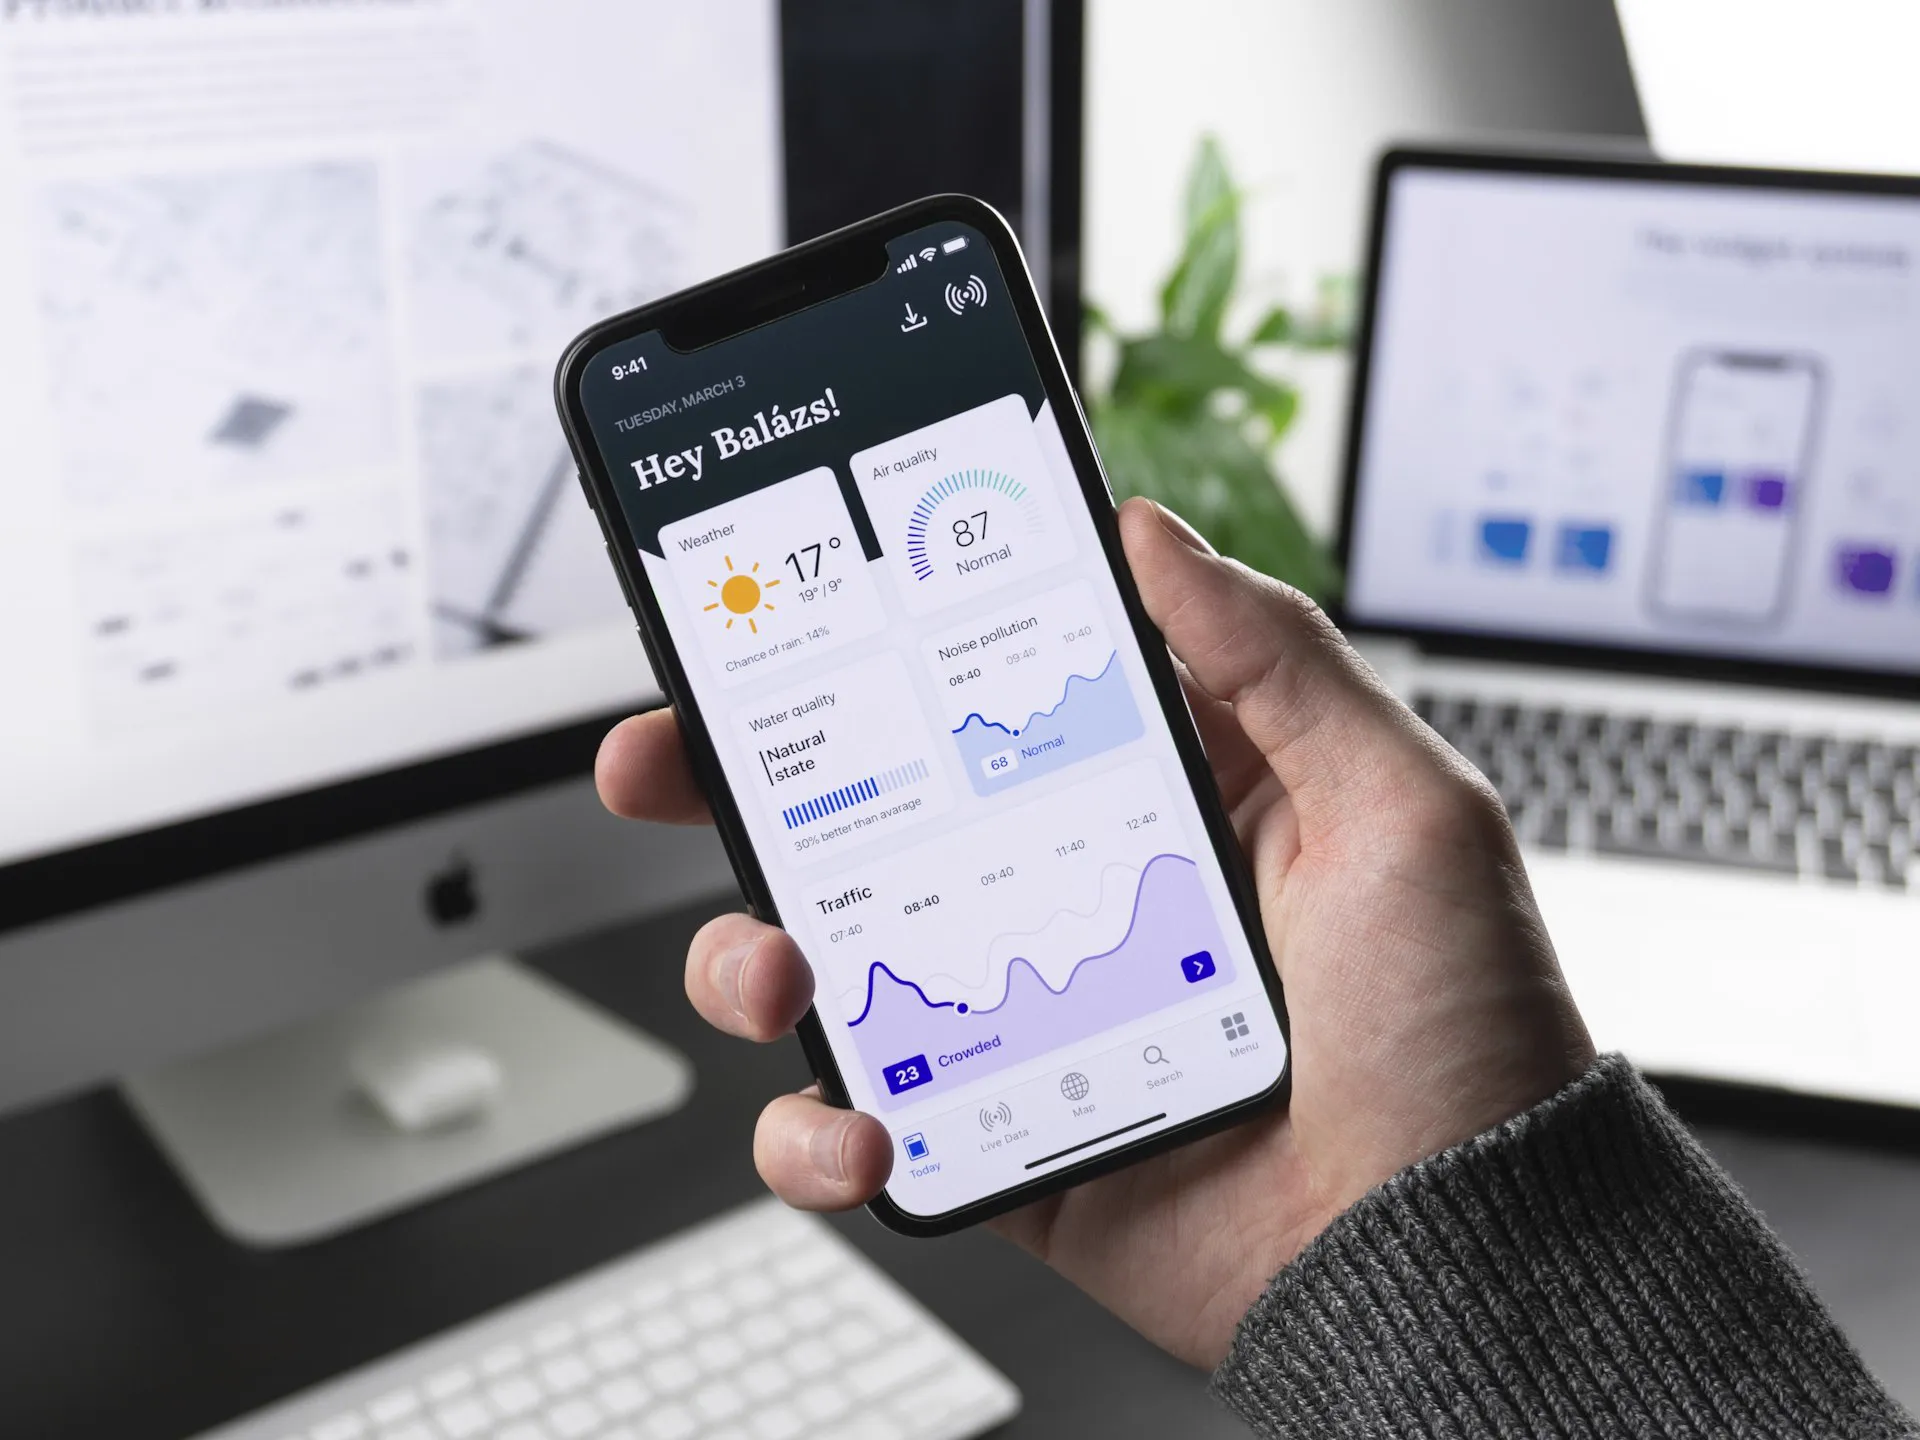
Mobile Application Security for a Marketplace
An account-takeover chain closed before 11 million users could be exposed to it.
Client name withheld by agreement- Client
- Consumer marketplace app
- Region
- United States
- Year
- 2025
- Duration
- 6 weeks
- Scope
- iOS, Android and 140 APIs
- Practice
- Offensive Security & Resilience
The challenge
What was at stake.
A consumer marketplace with millions of users was shipping new mobile features weekly. A bug bounty report hinted at account-takeover risk, but nobody had tested the app and its APIs end to end.
Customer trust was the product. One public account-takeover incident could undo years of growth.
What we did
The approach, step by step.
- 01
App and API testing
iOS and Android binaries and 140 APIs tested against the OWASP MASVS and API Security Top 10.
- 02
Attack chains
We chained an authorization flaw with a weak password-reset flow into a working account-takeover path.
- 03
Fix and verify
Engineers fixed the chain within days, and we verified each change before release.
- 04
Secure release gates
Security checks added to the mobile release pipeline so new features ship tested.
Outcomes
What changed, in numbers.
- 1
- account-takeover chain closed before exploitation
- 140
- APIs tested
- 11M
- users protected
- 2
- platforms covered: iOS and Android
They thought like an attacker and worked like part of our team.
Services delivered
Related engagements
More work in Offensive Security & Resilience.
-
 United States · 8 weeks
Offensive Security & Resilience · 2025Pre-Peak Penetration Testing for a National RetailerTwo critical payment-page exposures found and fixed six weeks before holiday trading.
-
 Gulf Coast, U.S. · 20 weeks
Offensive Security & Resilience · 2024OT-Safe Ransomware Resilience for an Energy UtilityRecovery time for core systems proven at under 18 hours, without touching live operations.
-
 Dallas, Texas · 24 weeks
Offensive Security & Resilience · 2025 · OngoingOne Evidence Model for a Fintech LenderFour frameworks mapped to one control set, with audit evidence requests down by two thirds.

Let’s talk about your version of this.
Share what you are up against. A senior practitioner who has delivered this kind of work will reply within one business day.